 SafeCadence
Security teams
Review exposure and policy findings with their source evidence and operational relevance.
NetRisk / Sample workspace
See what matters. Understand why. Decide what to do next.
NetRisk brings network assets, configuration evidence, exposure and business context into a reviewable security picture. It is designed for security, network and infrastructure teams who need to prioritize findings, not just collect another list of alerts.
AI at Scale. Humans in Control.
From evidence to a clearer decision
Start with authorized exports or an explicitly scoped source. Review what is observed, what is inferred and what is still unknown.
Start with supported configuration exports, inventory and security evidence. Source status and freshness matter.
Review assets, relationships, exposure and policy findings together where the supplied evidence supports it.
See the reason for a finding, its supporting evidence and any uncertainty or missing inputs.
Prepare a reviewer-ready recommendation or report. A finding is not an automatic change or proof of remediation.
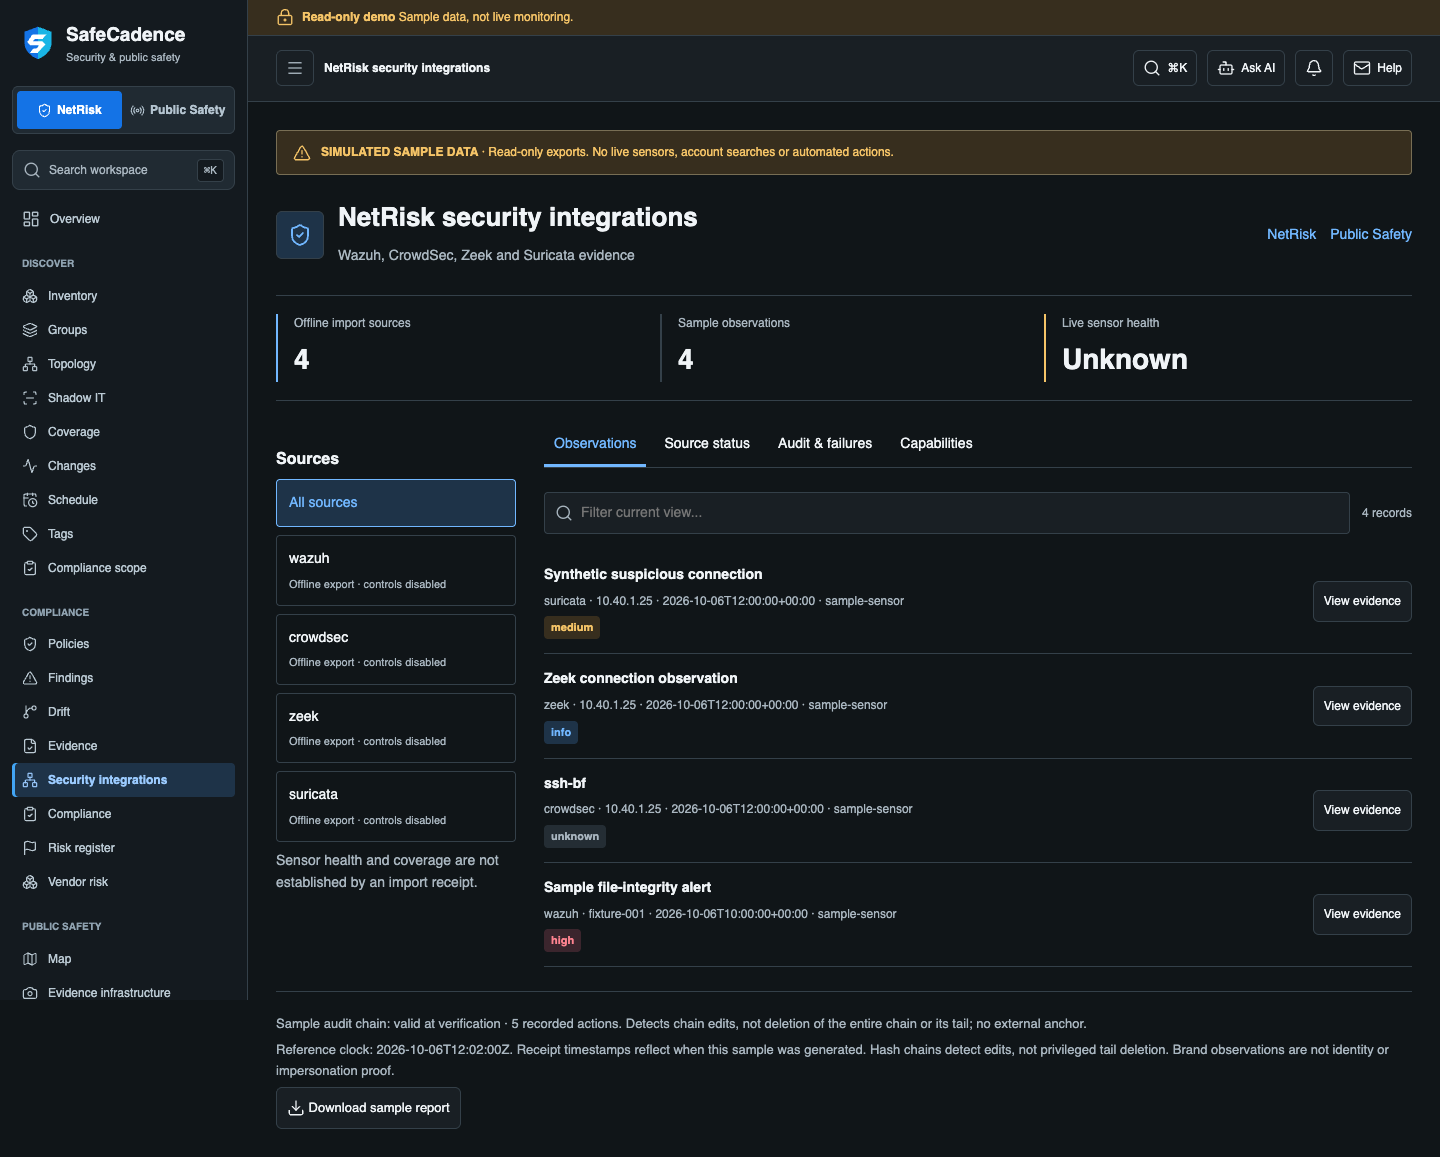
Review exposure and policy findings with their source evidence and operational relevance.
Bring configuration and topology context into security review without treating a parser result as a live device check.
See the issue, why it matters, what supports the assessment and what still needs validation.
The public workspace uses fictional data. It does not represent a live scan, connected customer sensors, universal vendor coverage or production-qualified remediation. Live integrations and customer-specific outcomes require separate qualification.
Open sample demoAgree on the mission, data access, owner and acceptance tests before connecting systems.